[Q177-Q197] Free Sample Questions to Practice SC-100 Certification Test Engine [Aug-2026]


Rate this post

Free Sample Questions to Practice SC-100 Certification Test Engine [Aug-2026]

2026 Valid SC-100 Real Exam Questions, practice Microsoft Certified: Cybersecurity Architect Expert

Microsoft SC-100 Exam Syllabus Topics:

Section Weight Objectives
Design security solutions for applications and data (20-25%) 22.5% – Design security for data

  • 1. Design a data classification and protection strategy
  • 2. Design a data retention and deletion strategy
  • 3. Design a strategy for securing data in transit, at rest, and in use

– Design security for applications

  • 1. Evaluate and design a secure application development lifecycle
  • 2. Design a strategy for securing third-party and open-source dependencies
  • 3. Design a strategy for application security testing
Design security operations, identity, and compliance capabilities (30-35%) 32.5% – Evaluate regulatory compliance

  • 1. Interpret compliance requirements and their technical capabilities
  • 2. Design infrastructure that complies with security and compliance requirements

– Design a security operations strategy

  • 1. Design a response strategy
  • 2. Design a threat detection strategy
  • 3. Design a logging and auditing strategy

– Design an identity security strategy

  • 1. Design a workload identity strategy
  • 2. Design an authorization strategy
  • 3. Design a user and administrator identity strategy
  • 4. Design an authentication strategy
Design security solutions for infrastructure (20-25%) 22.5% – Design security for SaaS, PaaS, and IaaS services

  • 1. Design security for Azure storage, SQL, and Cosmos DB
  • 2. Evaluate security baselines for SaaS, PaaS, and IaaS
  • 3. Design security for Azure Kubernetes Service

– Design security for server and client endpoints

  • 1. Specify security baselines for server and client endpoints
  • 2. Specify security for mobile devices and clients
  • 3. Specify security for Linux and Windows servers

– Design security for containers

  • 1. Evaluate and design security for container orchestration
  • 2. Evaluate and design security for containerized workloads
Design solutions that align with security best practices and priorities (20-25%) 22.5% – Evaluate security operations

  • 1. Evaluate security posture using Microsoft Defender for Cloud
  • 2. Evaluate security posture using Microsoft 365 Defender
  • 3. Evaluate security posture using Microsoft Sentinel
  • 4. Evaluate security posture using Microsoft Intune

– Design a Zero Trust strategy and architecture

  • 1. Evaluate and design an identity strategy
  • 2. Evaluate and design a application strategy
  • 3. Evaluate and design a infrastructure strategy
  • 4. Evaluate and design a network strategy
  • 5. Evaluate and design a data strategy


NO.177 Hotspot Question
You have an Azure subscription that contains 100 virtual machines. The virtual machines are accessed by using Azure Bastion.
You need to recommend a solution to ensure that only specific users in specific locations can access the virtual machines. The solution must meet the following requirements:
– Restrict access to the virtual machines based on an originating IP
address or a connection request by using just-in-time (JIT) VM access
network-based controls.
– Restrict access to the virtual machines based on role-based access
control (RBAC) role assignments by using JIT VM access authorization
controls.
Which Microsoft cloud services should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
NO.178 You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You need to enforce ISO 27001:2013 standards for new resources deployed to the subscription.
The solution must ensure that noncompliant resources are automatically detected.
What should you use?


NO.179 Your company wants to optimize using Azure to protect its resources from ransomware.
You need to recommend which capabilities of Azure Backup and Azure Storage provide the strongest protection against ransomware attacks. The solution must follow Microsoft Security Best Practices.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.180 You are designing a security operations strategy based on the Zero Trust framework.
You need to increase the operational efficiency of the Microsoft Security Operations Center (SOC).
Based on the Zero Trust framework, which three deployment objectives should you prioritize in sequence? To answer, move the appropriate objectives from the list of objectives to the answer area and arrange them in the correct order.

NO.181 You plan to deploy a dynamically scaling, Linux-based Azure Virtual Machine Scale Set that will host jump servers. The jump servers will be used by support staff who connect f personal and kiosk devices via the internet. The subnet of the jump servers will be associated to a network security group (NSG) You need to design an access solution for the Azure Virtual Machine Scale Set. The solution must meet the following requirements:
* Ensure that each time the support staff connects to a jump server; they must request access to the server.
* Ensure that only authorized support staff can initiate SSH connections to the jump servers.
* Maximize protection against brute-force attacks from internal networks and the internet.
* Ensure that users can only connect to the jump servers from the internet.
* Minimize administrative effort
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.182 You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

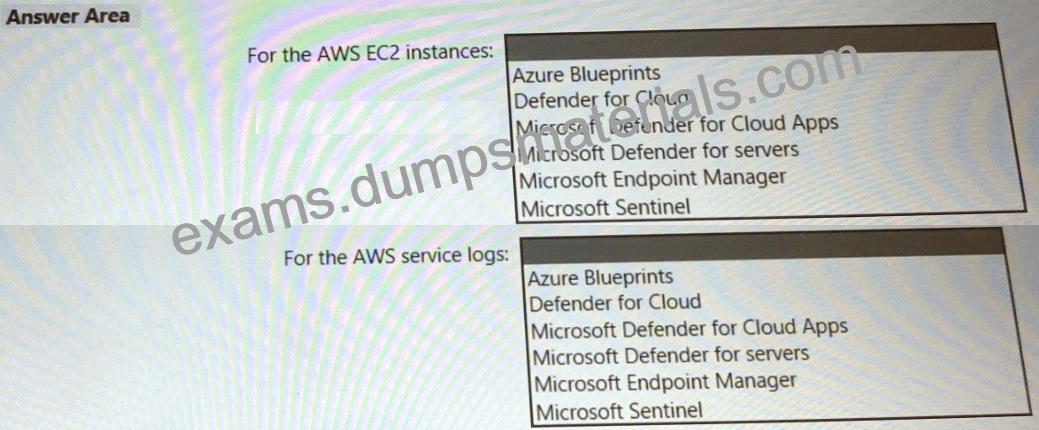
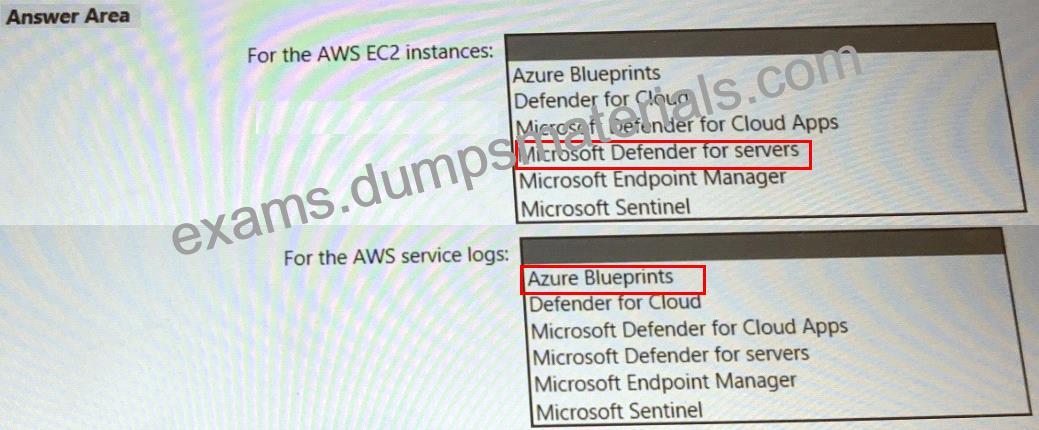
NO.183 You need to recommend a solution to meet the AWS requirements.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.184 You have a Microsoft 365 subscription.
You are designing a user access solution that follows the Zero Trust principles of the Microsoft Cybersecurity Reference Architectures (MCRA).
You need to recommend a solution that automatically restricts access to Microsoft Exchange Online.
SharePoint Online, and Teams m near-real-lime (NRT) in response to the following Azure AD events:
* A user account is disabled or deleted
* The password of a user is changed or reset.
* All the refresh tokens for a user are revoked
* Multi-factor authentication (MFA) is enabled for a user
Which two features should you include in the recommendation? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.


NO.185 You need to recommend a multi-tenant and hybrid security solution that meets to the business requirements and the hybrid requirements. What should you recommend? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.

NO.186 You plan to deploy a dynamically scaling, Linux-based Azure Virtual Machine Scale Set that will host jump servers. The jump servers will be used by support staff who connect f personal and kiosk devices via the internet. The subnet of the jump servers will be associated to a network security group (NSG) You need to design an access solution for the Azure Virtual Machine Scale Set. The solution must meet the following requirements:
* Ensure that each time the support staff connects to a jump server; they must request access to the server.
* Ensure that only authorized support staff can initiate SSH connections to the jump servers.
* Maximize protection against brute-force attacks from internal networks and the internet.
* Ensure that users can only connect to the jump servers from the internet.
* Minimize administrative effort
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.187 Your company has an on-premises network, an Azure subscription, and a Microsoft 365 E5 subscription. The company uses the following devices:
* Computers that run either Windows 10 or Windows 11
* Tablets and phones that run either Android or iOS
You need to recommend a solution to classify and encrypt sensitive Microsoft Office 365 data regardless of where the data is stored. What should you include in the recommendation?


NO.188 Case Study 1 – Fabrikam, Inc
OverView
Fabrikam, Inc. is an insurance company that has a main office in New York and a branch office in Paris.
Existing Environment
On-premises Environment
The on-premises network contains a single Active Directory Domain Services (AD DS) domain named corp.fabrikam.com.
Azure Environment
Fabrikam has the following Azure resources:
– A Microsoft Entra tenant named fabrikam.onmicrosoft.com that syncs with corp.fabrikam.com
– A single Azure subscription named Sub1
– A virtual network named Vnet1 in the East US Azure region
– A virtual network named Vnet2 in the West Europe Azure region
– An instance of Azure Front Door named FD1 that has Azure Web Application Firewall (WAF) enabled
– A Microsoft Sentinel workspace
– An Azure SQL database named ClaimsDB that contains a table named ClaimDetails
– 20 virtual machines that are configured as application servers and are NOT onboarded to Microsoft Defender for Cloud
– A resource group named TestRG that is used for testing purposes only
– An Azure Virtual Desktop host pool that contains personal assigned session hosts
– All the resources in Sub1 are in either the East US or the West Europe region.
Partners
Fabrikam has contracted a company named Contoso, Ltd. to develop applications. Contoso has the following infrastructure:
– An Microsoft Entra named contoso.onmicrosoft.com
– An Amazon Web Services (AWS) implementation named ContosoAWS1 that contains AWS EC2 instances used to host test workloads for the applications of Fabrikam Developers at Contoso will connect to the resources of Fabrikam to test or update applications.
The developers will be added to a security Group named Contoso Developers in fabrikam.onmicrosoft.com that will be assigned to roles in Sub1. The ContosoDevelopers group is assigned the db.owner role for the ClaimsDB database.
Compliance Event
Fabrikam deploys the following compliance environment:
– Defender for Cloud is configured to assess all the resources in Sub1 for compliance to the HIPAA HITRUST standard.
– Currently, resources that are noncompliant with the HIPAA HITRUST standard are remediated manually.
– Qualys is used as the standard vulnerability assessment tool for servers.
Problem Statements
The secure score in Defender for Cloud shows that all the virtual machines generate the following recommendation. Machines should have a vulnerability assessment solution. All the virtual machines must be compliant in Defender for Cloud.
ClaimApp Deployment
Fabrikam plans to implement an internet-accessible application named ClaimsApp that will have the following specification
– ClaimsApp will be deployed to Azure App Service instances that connect to Vnet1 and Vnet2.
– Users will connect to ClaimsApp by using a URL of https://claims.fabrikam.com.
– ClaimsApp will access data in ClaimsDB.
– ClaimsDB must be accessible only from Azure virtual networks.
– The app services permission for ClaimsApp must be assigned to ClaimsDB.
Application Development Requirements
Fabrikam identifies the following requirements for application development:
– Azure DevTest labs will be used by developers for testing.
– All the application code must be stored in GitHub Enterprise.
– Azure Pipelines will be used to manage application deployments.
– All application code changes must be scanned for security vulnerabilities, including application code or configuration files that contain secrets in clear text. Scanning must be done at the time the code is pushed to a repository.
Security Requirement
Fabrikam identifies the following security requirements:
– Internet-accessible applications must prevent connections that originate in North Korea.
– Only members of a group named InfraSec must be allowed to configure network security groups (NSGs} and instances of Azure Firewall, VJM. And Front Door in Sub1.
– Administrators must connect to a secure host to perform any remote administration of the virtual machines. The secure host must be provisioned from a custom operating system image.
AWS Requirements
Fabrikam identifies the following security requirements for the data hosted in ContosoAWSV.
– Notify security administrators at Fabrikam if any AWS EC2 instances are noncompliant with secure score recommendations.
– Ensure that the security administrators can query AWS service logs directly from the Azure environment.
Contoso Developer Requirements
Fabrikam identifies the following requirements for the Contoso developers:
– Every month, the membership of the ContosoDevelopers group must be verified.
– The Contoso developers must use their existing contoso.onmicrosoft.com credentials to access the resources in Sub1.
– The Comoro developers must be prevented from viewing the data in a column named MedicalHistory in the ClaimDetails table.
Compliance Requirement
Fabrikam wants to automatically remediate the virtual machines in Sub1 to be compliant with the HIPPA HITRUST standard. The virtual machines in TestRG must be excluded from the compliance assessment.
You need to recommend a solution to scan the application code. The solution must meet the application development requirements.
What should you include in the recommendation?


NO.189 You are designing a ransomware response plan that follows Microsoft Security Best Practices.
You need to recommend a solution to minimize the risk of a ransomware attack encrypting local user files.
What should you include in the recommendation?


NO.190 You need to recommend a security methodology for a DevOps development process based on the Microsoft Cloud Adoption Framework for Azure.
During which stage of a continuous integration and continuous deployment (CI/CD) DevOps process should each security-related task be performed? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point

NO.191 You have an Azure subscription that has Microsoft Defender for Cloud enabled. You have an Amazon Web Services (AWS) implementation.
You plan to extend the Azure security strategy to the AWS implementation. The solution will NOT use Azure Arc. Which three services can you use to provide security for the AWS resources? Each correct answer presents a complete solution. NOTE: Each correct selection is worth one point.


NO.192 Your company is moving all on-premises workloads to Azure and Microsoft 365. You need to design a security orchestration, automation, and response (SOAR) strategy in Microsoft Sentinel that meets the following requirements:
* Minimizes manual intervention by security operation analysts
* Supports Waging alerts within Microsoft Teams channels
What should you include in the strategy?


NO.193 Your company is preparing for cloud adoption.
You are designing security for Azure landing zones.
Which two preventative controls can you implement to increase the secure score? Each NOTE:
Each correct selection is worth one point.


NO.194 You need to recommend a multi-tenant and hybrid security solution that meets to the business requirements and the hybrid requirements. What should you recommend? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

NO.195 You need to recommend a solution to evaluate regulatory compliance across the entire managed environment. The solution must meet the regulatory compliance requirements and the business requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.196 You need to recommend a solution to meet the compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

NO.197 You have an Azure subscription that is used as an Azure landing zone for an application. You need to evaluate the security posture of all the workloads in the landing zone. What should you do first?


Genuine SC-100 Exam Dumps Free Demo Valid QA’s: https://www.dumpsmaterials.com/SC-100-real-torrent.html


Related Links: myportal.utt.edu.tt www.stes.tyc.edu.tw myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt www.stes.tyc.edu.tw

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below