[Q274-Q296] Updated Oct-2026 Test Engine to Practice Test for SC-300 Exam Questions and Answers!


Rate this post

Updated Oct-2026 Test Engine to Practice Test for SC-300 Exam Questions and Answers!

Microsoft Identity and Access Administrator Certification Sample Questions and Practice Exam

Microsoft SC-300 exam covers a wide range of topics, including identity and access management, authentication and authorization, identity governance, and more. SC-300 exam consists of multiple-choice questions and simulations, which require you to demonstrate your skills in real-world scenarios. SC-300 exam is designed to test your knowledge of Microsoft technologies such as Azure Active Directory, Microsoft 365, and Microsoft Identity Manager.


Q274. You need to configure the assignment of Azure AD licenses to the Litware users. The solution must meet the licensing requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Q275. You have 2,500 users who are assigned Microsoft Office 365 Enterprise E3 licenses. The licenses are assigned to individual users.
From the Groups blade in the Azure Active Directory admin center, you assign Microsoft 365 Enterprise E5 licenses to the users.
You need to remove the Office 365 Enterprise E3 licenses from the users by using the least amount of administrative effort.
What should you use?


Q276. You have a custom cloud app named App1 that is registered in Azure Active Directory (Azure AD).
App1 is configured as shown in the following exhibit.

Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.

Q277. You have a Microsoft Entra tenant that contains the users shown in the following table:

Admin4 creates a Conditional Access policy named Policy1 by using the “Require multifactor authentication for Azure management” template.
Which users will be required to use multi-factor authentication (MFA) the next time they sign in?


Q278. You have a Microsoft 365 tenant and an Active Directory domain named adatum.com.
You deploy Azure AD Connect by using the Express Settings.
You need to configure self-service password reset (SSPR) to meet the following requirements:
* When users reset their password, they must be prompted to respond to a mobile app notification or answer three predefined security questions.
* Passwords must be synced between the tenant and the domain regardless of where the password was reset.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q279. You have an Azure Active Directory (Azure AD) tenant that has an Azure Active Directory Premium Plan 2 license. The tenant contains the users shown in the following table.
You have the Device Settings shown in the following exhibit.

User1 has the devices shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE:Each correct selection is worth one point.

Q280. You have an Azure subscription that contains the resources shown in the following table.
You need to configure access to Vault1. The solution must meet the following requirements:
* Ensure that User1 can manage and create keys in Vault1.
* Ensure that User2 can access a certificate stored in Vault1.
* Use the principle of least privilege.
Which role should you assign to each user? To answer select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q281. You have an Azure Active Directory (Azure AD) tenant that contains an administrative unit named Department1.
Department1 has the users shown in the Users exhibit. (Click the Users tab.)

Department1 has the groups shown in the Groups exhibit. (Click the Groups tab.)

Department1 has the user administrator assignments shown in the Assignments exhibit. (Click the Assignments tab.)

The members of Group2 are shown in the Group2 exhibit. (Click the Group2 tab.)

For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

Q282. You have a Microsoft 365 tenant and an Active Directory domain named adatum.com.
You deploy Azure AD Connect by using the Express Settings.
You need to configure self-service password reset (SSPR) to meet the following requirements:
* When users reset their password, they must be prompted to respond to a mobile app notification or answer three predefined security questions.
* Passwords must be synced between the tenant and the domain regardless of where the password was reset.
What should you do? To answer, select the appropriate options in the answer area.
NOTE:Each correct selection is worth one point.

Q283. You need to support the planned changes and meet the technical requirements for MFA.
Which feature should you use, and how long before the users must complete the registration? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q284. You need to meet the technical requirements for the probability that user identities were compromised.
What should the users do first, and what should you configure? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q285. You have a Microsoft Entra tenant that contains the users shown in the following table.

You have a user risk policy that has the following settings:
* Assignments:
o Include: Group1
o Exclude: Group2
* Sign-in risk Medium and above
* Access controls:
o Grant access: Require password change
When the users attempt to sign in. user risk levels are detected as shown in the following table.

For each of the following statements, select Yes if the statement is true. Otherwise, select No.

Q286. You have an Azure AD tenant that contains a user named User1 and the conditional access policies shown in the following table.

You need to evaluate which policies will be applied User1 when User1 attempts to sign-in from various IP addresses.
Which feature should you use?


Q287. You have a Microsoft 365 tenant.
You need to Identity users who have leaked credentials. The solution must meet the following requirements:
* Identity sign-ms by users who are suspected of having leaked credentials.
* Flag the sign-ins as a high-risk event.
* Immediately enforce a control to mitigate the risk, while still allowing the user to access applications.
What should you use? To answer, select the appropriate options m the answer area.

Q288. You have an on-premises app named App1.
You have a Microsoft Entra tenant.
You plan to publish App1 by using Microsoft Entra Private Access.
You need to enable the Private access profile.
Which blade should you use in the Microsoft Entra admin center?


Q289. You have an Azure Active Directory (Azure AD) tenant named contoso.com that contains a user named User1.
User1 has the devices shown in the following table.

On November 5, 2020, you create and enforce terms of use in contoso.com that has the following settings:
Name: Terms1
Display name: Contoso terms of use
Require users to expand the terms of use: On
Require users to consent on every device: On
Expire consents: On
Expire starting on: December 10, 2020
Frequency: Monthly
On November 15, 2020, User1 accepts Terms1 on Device3.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.

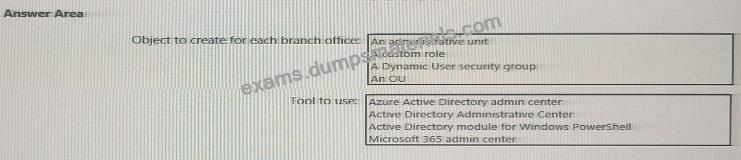
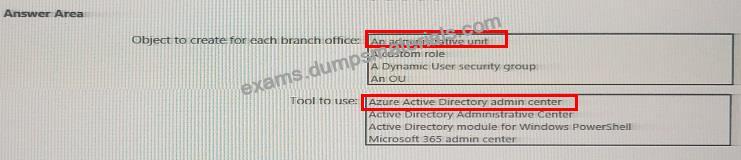
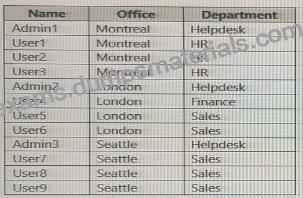
Q290. You need to meet the technical requirements for license management by the helpdesk administrators.
What should you create first, and which tool should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q291. You have an Azure Active Directory (Azure AD) tenant named contoso.com.
You need to ensure that Azure AD External Identities pricing is based on monthly active users (MAU).
What should you configure?


Q292. You have an Azure AD tenant and an Azure web app named App1.
You need to provide guest users with self-service sign-up for App1. The solution must meet the following requirements:
* Guest users must be able to sign up by using a one-time password.
* The users must provide their first name, last name, city, and email address during the sign-up process.
What should you configure in the Azure Active Directory admin center for each requirement? To answer, select the appropriate options in the answer are a.
NOTE: Each correct selection is worth one point.

Q293. You have an on-premises Microsoft Exchange organization that uses an SMTP address space of contoso.com.
You discover that users use their email address for self-service sign-up to Microsoft 365 services.
You need to gain global administrator privileges to the Azure Active Directory (Azure AD) tenant that contains the self-signed users.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.

Q294. You have an AzureAD tenant that contains the users shown in the following table.

You have the locations shown in the following table.

The tenantcontainsa named location that Das the following configurations:
* Name: location1
* Mark as trusted location: Enabled
* IPv4 range: 10.10.0.0/16
MFA has a trusted iPad dress range of 193.17.17.0/24.
You have a Conditional Access policy that has the following settings:
* Name: CAPolicy1
* Assignments
o Users or workload identities: Group 1
o Cloud apps or actions: All cloud apps
* Conditions
* Locations All trusted locations
* Access controls
o Gant
* Grant access: Require multi-factor authentication
Session: 0 controls selected
* Enable policy: On
For each of the following statements select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.

Q295. You have an on-premises datacenter that contains the hosts shown in the following table.

You have an Azure Active Directory (Azure AD) tenant that syncs to the Active Directory forest. Multi-factor authentication (MFA) is enforced for Azure AD.
You need to ensure that you can publish App1 to Azure AD users.
What should you configure on Server and Firewall1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.

Q296. You have a Microsoft 365 tenant.
You need to ensure that you tan view Azure Active Directory (Azure AD) audit log information by using Azure Monitor.
What should you do first?


Microsoft SC-300 Exam covers a range of topics related to identity and access management, including configuring and managing Azure Active Directory, implementing identity solutions, managing access, and securing identities. It is designed to test the skills and knowledge of IT professionals who work with Microsoft technologies and want to demonstrate their expertise in managing identity and access solutions in a secure and efficient manner. By passing SC-300 exam and earning the certification, IT professionals can showcase their skills and knowledge to potential employers and advance their careers in the field of IT security.


Certification dumps Microsoft Certified: Identity and Access Administrator Associate SC-300 guides – 100% valid: https://www.dumpsmaterials.com/SC-300-real-torrent.html


Related Links: myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below