SY0-701 Pre-Exam Practice Tests (Updated 1265 Questions) [Q684-Q701]


Rate this post

SY0-701 Pre-Exam Practice Tests | (Updated 1265 Questions)

Valid SY0-701 Exam Q&A PDF – One Year Free Update

CompTIA SY0-701 Exam Syllabus Topics:

Topic Details
Topic 1
  • Threats, Vulnerabilities, and Mitigations: In this topic, you’ll find discussions comparing threat actors and motivations, explaining common threat vectors and attack surfaces, and outlining different types of vulnerabilities. Moreover, the topic focuses on analyzing indicators of malicious activity in scenarios and exploring mitigation techniques used to secure enterprises against threats.
Topic 2
  • General Security Concepts: This topic covers various types of security controls, fundamental security concepts, the importance of change management processes in security, and the significance of using suitable cryptographic solutions.
Topic 3
  • Security Architecture: Here, you’ll learn about security implications across different architecture models, applying security principles to secure enterprise infrastructure in scenarios, and comparing data protection concepts and strategies. The topic also delves into the importance of resilience and recovery in security architecture.
Topic 4
  • Security Program Management and Oversight: Finally, this topic discusses elements of effective security governance, the risk management process, third-party risk assessment, and management processes. Additionally, the topic focuses on security compliance requirements, types and purposes of audits and assessments, and implementing security awareness practices in various scenarios.
Topic 5
  • Security Operations: This topic delves into applying common security techniques to computing resources, addressing security implications of proper hardware, software, and data asset management, managing vulnerabilities effectively, and explaining security alerting and monitoring concepts. It also discusses enhancing enterprise capabilities for security, implementing identity and access management, and utilizing automation and orchestration for secure operations.


NEW QUESTION 684
A user needs to complete training at https://comptiatraining.com. After manually entering the URL, the user sees that the accessed website is noticeably different from the standard company website. Which of the following is the most likely explanation for the difference?


NEW QUESTION 685
An attacker posing as the Chief Executive Officer calls an employee and instructs the employee to buy gift cards. Which of the following techniques is the attacker using?


NEW QUESTION 686
A systems administrator just purchased multiple network devices. Which of the following should the systems administrator perform to prevent attackers from accessing the devices by using publicly available information?


NEW QUESTION 687
Which of the following agreements defines response time, escalation, and performance metrics?


NEW QUESTION 688
An employee emailed a new systems administrator a malicious web link and convinced the administrator to change the email server’s password. The employee used this access to remove the mailboxes of key personnel.
Which of the following security awareness concepts would help prevent this threat in the future?


NEW QUESTION 689
A company makes a change during the appropriate change window, but the unsuccessful change extends beyond the scheduled time and impacts customers. Which of the following would prevent this from reoccurring?


NEW QUESTION 690
A spoofed identity was detected for a digital certificate. Which of the following are the type of unidentified key and the certificate mat could be in use on the company domain?


NEW QUESTION 691
A security analyst needs to improve the company’s authentication policy following a password audit. Which of the following should be included in the policy? (Select two).


NEW QUESTION 692
A business uses Wi-Fi with content filleting enabled. An employee noticed a coworker accessed a blocked sue from a work computer and repotted the issue. While Investigating the issue, a security administrator found another device providing internet access to certain employees. Which of the following best describes the security risk?


NEW QUESTION 693
A security administrator is addressing an issue with a legacy system that communicates data using an unencrypted protocol to transfer sensitive data to a third party. No software updates that use an encrypted protocol are available, so a compensating control is needed. Which of the following are the most appropriate for the administrator to suggest? (Select two.)


NEW QUESTION 694
Which of the following is a reason an organization should use different CSPs for a critical financial application?


NEW QUESTION 695
Which of the following is a preventive physical security control?


NEW QUESTION 696
While analyzing SIEM alerts for a company’s WAF, an incident response analyst observes the following:
https://corporate-A.com/loadimage?filename=/etc/
https://corporate-A.com/loadimage?filename=../../etc/passwd
https://corporate-A.com/loadimage?filename=./etc/passwd
Which of the following best describes the observed behavior?


NEW QUESTION 697
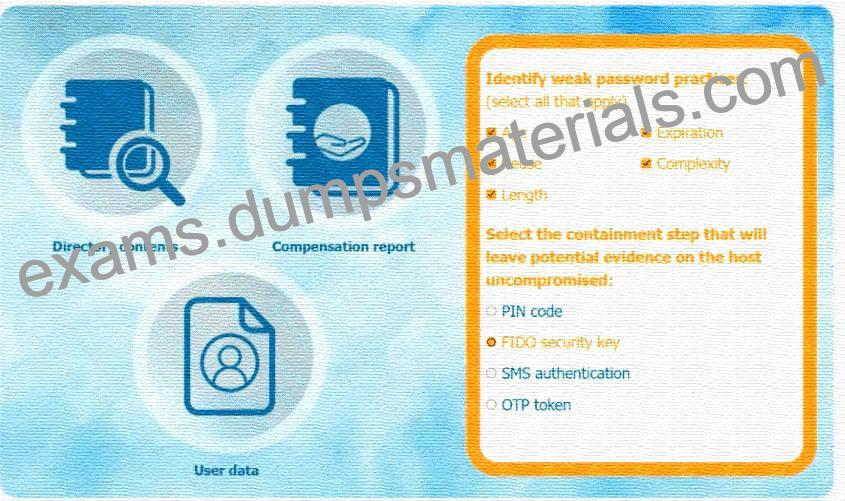
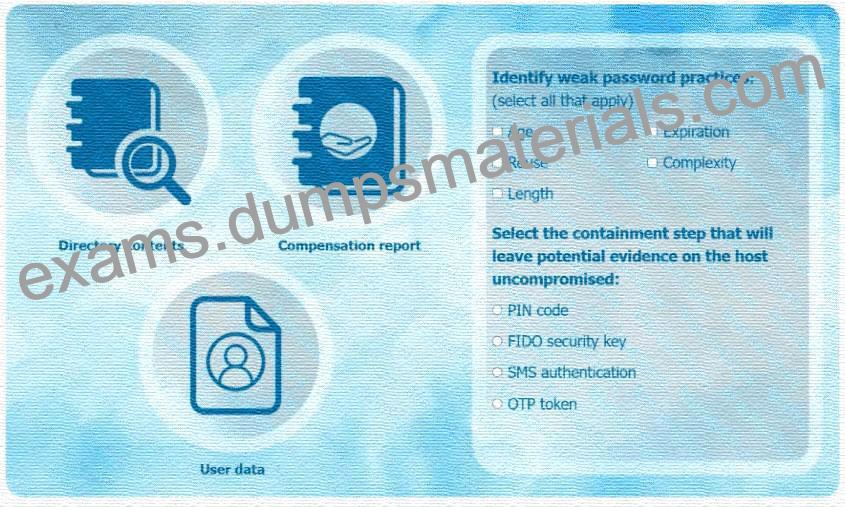
An organization has learned that its data is being exchanged on the dark web. The CIO has requested that you investigate and implement the most secure solution to protect employee accounts.
INSTRUCTIONS
Review the data to identify weak security practices and provide the most appropriate security solution to meet the CIO’s requirements.
NEW QUESTION 698
Which of the following is the best reason to perform a tabletop exercise?


NEW QUESTION 699
An organization experiences a cybersecurity incident involving a command-and-control server. Which of the following logs should be analyzed to identify the impacted host? (Select two).


NEW QUESTION 700
Which of the following is the best way to prevent data from being leaked from a secure network that does not need to communicate externally?


NEW QUESTION 701
Which of the following is a key reason to follow data retention policies during asset decommissioning?


CompTIA Security+ Certification Exam Free Update Certification Sample Questions: https://www.dumpsmaterials.com/SY0-701-real-torrent.html


Related Links: myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt myportal.utt.edu.tt

Leave a Reply

Your email address will not be published. Required fields are marked *

Enter the text from the image below